Anthropic expands verified security access through three tiers
The revised program combines existing efforts and matches model access to the scope of authorized security work.
THE STORY IN THREE POINTS
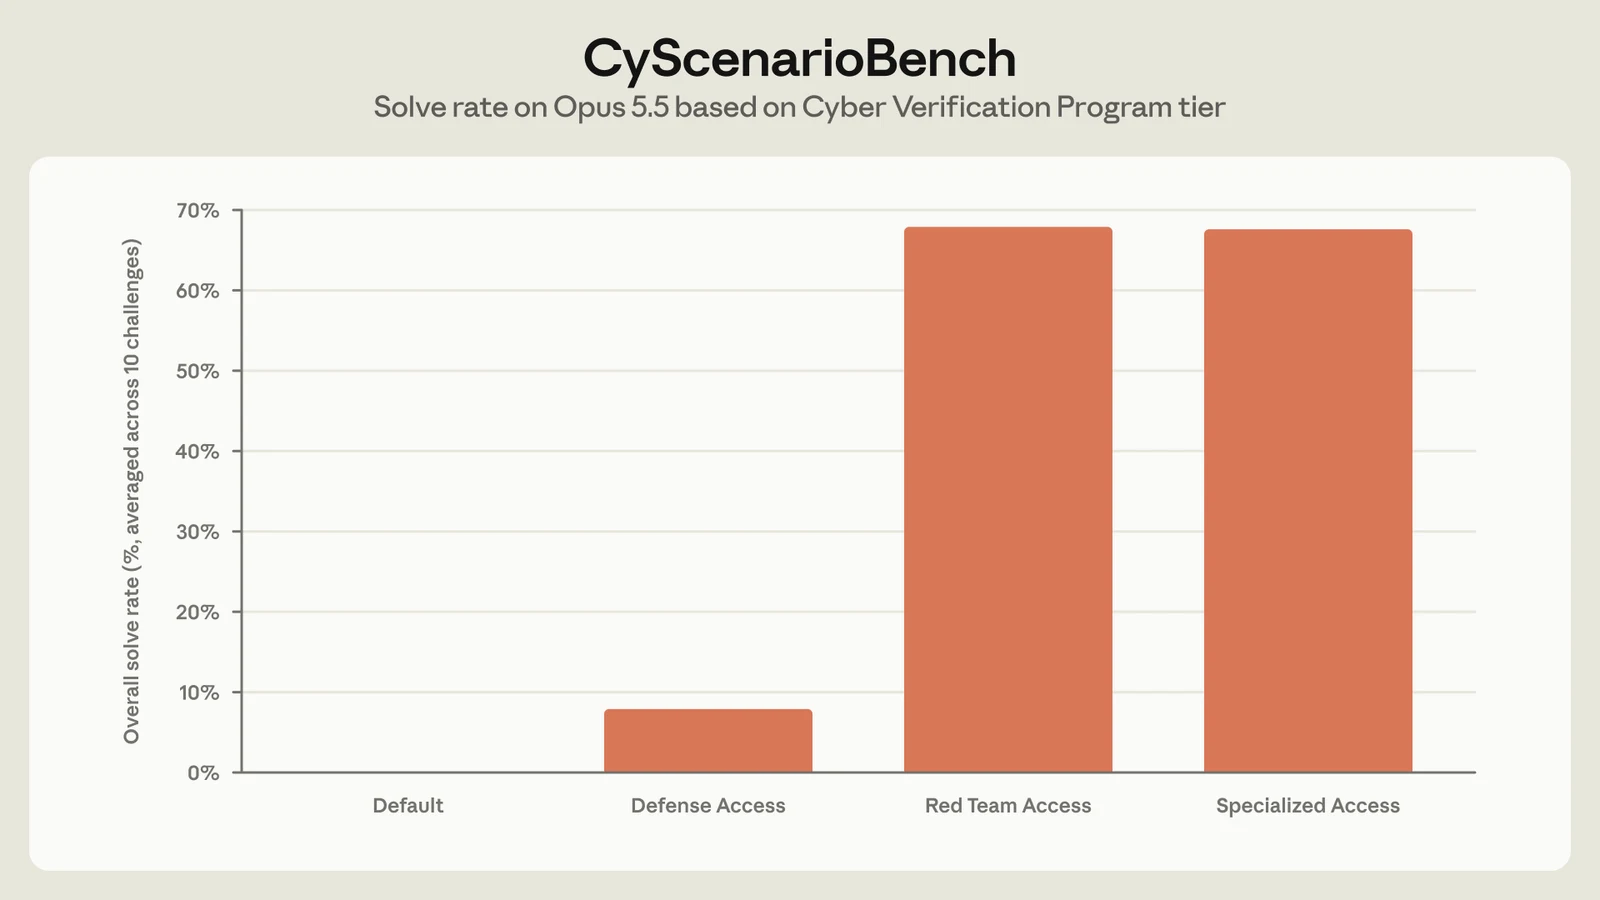
- The expanded program has Defense, Red Team and Specialized Access tiers.
- Verification requirements and controls differ by tier.
- Project Glasswing is being integrated into the offering.
The access change
Anthropic expanded its Cyber Verification Program into three tiers: Defense Access, Red Team Access and Specialized Access. It says the new offering combines earlier verification work with Project Glasswing.
The tiers differ in permitted scope, verification requirements and security controls. Authorized penetration testing sits above defensive work, while access involving high-risk systems is reserved for a limited set of vetted organizations. Application review and approval remain part of the program.
Editorial context: scope should travel with the task
For a security team, authorization needs to identify which systems it may test and what actions are allowed. A model's technical ability to attempt something does not establish that the organization has permission to do it.
An evaluation of tiered access could examine both valid work and requests that cross the assigned scope. That would test whether the controls preserve useful defensive work while keeping restrictions understandable to the people using the service.
Editorial outlook: what to watch
Useful follow-up would describe application processing, false blocks and the practical review burden on security teams.
Readers should consult current program documentation for eligibility and data handling details. An announcement of broader access does not mean every applicant or every proposed security task will qualify.
Sources: Anthropic: Expanding the Cyber Verification Program ↗